Why I built SecretStash
By Doug Niccum, founder of SecretStash
I built SecretStash because small teams still share .env files over Slack and email, and nothing in between fit. AWS Secrets Manager and HashiCorp Vault took too long to set up, and enterprise platforms charge per seat. SecretStash encrypts each value on your machine and syncs it with one CLI command, for a flat $10/month.
Doug Niccum builds developer tools through Doug Niccum Design, LLC, the software company behind SecretStash.
When Doug onboarded at Henry Schein One this past January, one of the most stressful parts of the first few days wasn't the people or the process—it was configuring a new development environment without the database backups, API keys, and SSL certificates it depended on. Like most engineers, he'd relied on Slack and Teams to pass sensitive values between teammates, and knew it wasn't right, even when it felt quick.
The data backed up the gut feeling: GitGuardian's State of Secrets Sprawl report found that incidents in collaboration tools like Slack, Jira, and Confluence are more likely to be rated highly critical than incidents in source code, and a growing share of leaks now start outside the codebase entirely.
Existing options didn't fit either. AWS Secrets Manager and HashiCorp Vault took too long to set up for a small team. Self-hosted, open-source tools risked being abandoned. Enterprise secrets platforms were priced and built for organizations much larger than his.
So he built SecretStash—a CLI-first tool that lets developers store, share, and sync environment variables with client-side encryption, without the setup overhead of enterprise tooling. It's the tool he wished he'd had on day one.
Who is SecretStash for?
Small development teams who share .env files today, usually over Slack, email, or a shared doc. It fits teams of 2 to 20 people best, and the Organization plan has no user cap for teams that grow past that.
The Team plan is a flat $10/month for up to 20 users, and the Organization plan is a flat $40/month for unlimited users. You pay the same whether you add one teammate or ten, so onboarding someone never means another seat to approve.
It is built CLI-first for Laravel teams. You install it with Composer and pull variables with an Artisan command, and an npm package covers Node projects.
How does SecretStash keep secrets private?
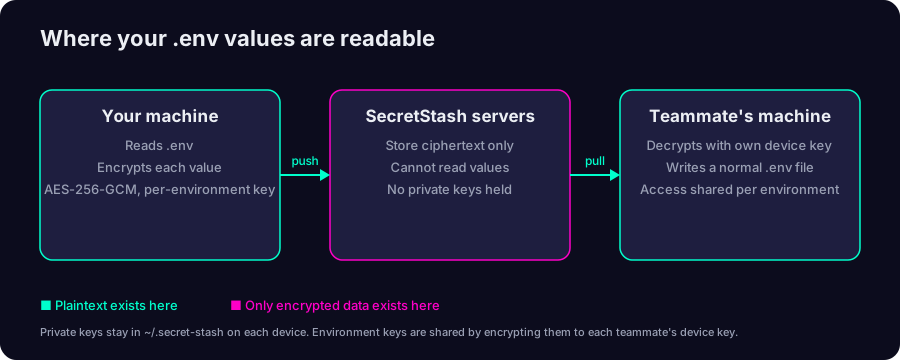
Every value is encrypted on your machine before it is sent, and SecretStash stores only the encrypted result. Our servers cannot read your raw secrets.
Each environment (local, staging, production) has its own encryption key. Each device gets its own key pair, and its private key stays on that device in ~/.secret-stash/device_private_key.pem. Values are encrypted with AES-256-GCM.
Giving a teammate access means encrypting the environment key for their device with php artisan secret-stash:share, once per environment. Nothing is sent in plain text along the way.
The tradeoff: if every device with access loses its key, we cannot recover the values for you. Generate a recovery key with php artisan secret-stash:keys recovery and keep it somewhere safe.
Why is SecretStash CLI-first?
Because developers already live in the terminal, and a .env file is what their apps already read. Pulling variables writes a normal .env file, so nothing in your application code changes.
The same command works on a laptop and in a CI/CD pipeline. A new teammate runs one pull instead of waiting for someone to paste values into a DM.
The web dashboard is there for creating applications and environments, inviting teammates, and reviewing what is stored.
How do you get started?
Create an account and a new organization, which starts with a 14-day trial. Add an application in the dashboard, then create an environment for each place your app runs.
In a Laravel project, run composer require dniccum/secret-stash-cli, then php artisan secret-stash:login to connect the CLI to your account. Set SECRET_STASH_APPLICATION_ID in your .env, then run php artisan secret-stash:install to create your device key.
Push your existing .env file with php artisan secret-stash:variables push, and teammates pull it with php artisan secret-stash:variables pull.
What doesn't SecretStash do yet?
It is not SOC 2 certified. SAML SSO is labeled "Coming Soon" and is not available on any plan yet.
Automatic secret rotation and dynamic secrets are not planned. SecretStash stores static environment variables.
Can you take your secrets with you if you leave?
Yes. Anyone with CLI access can pull the current values for any environment into a local .env file at any time.
That is the same pull command your team runs every day, so leaving never depends on a special export tool or a support ticket.
Who runs SecretStash?
SecretStash is built and run by Doug Niccum Design, LLC. Questions about security, billing, or a missing feature go to support@secretstash.cloud.
How long has SecretStash been around?
Development started in October 2025, and SecretStash launched publicly in 2026. It is still actively developed.